
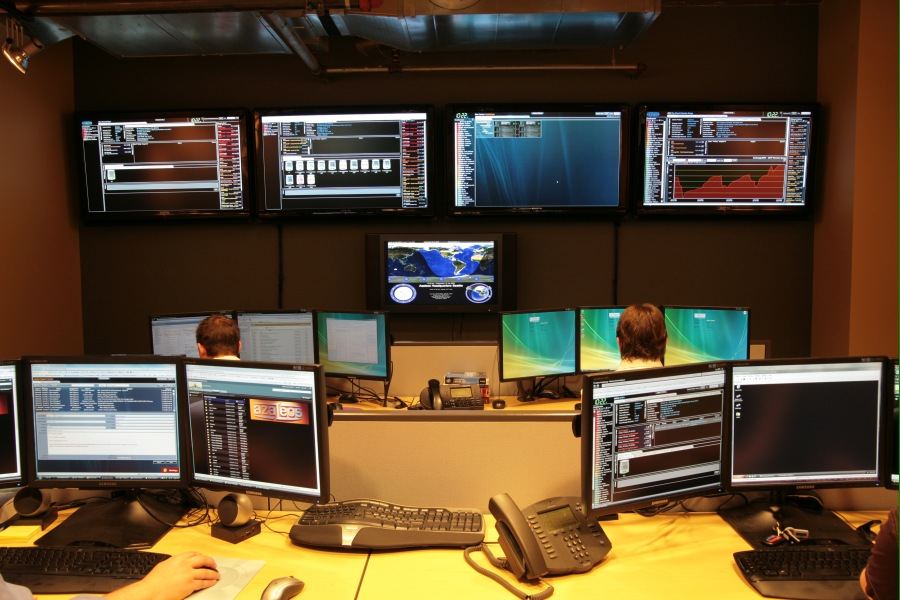
Cyber security operations centres are adopting faster detection tools as attacks arrive in shorter bursts and target a wider range of organisations. Modern platforms combine network traffic, login records and device alerts into a single view, helping analysts spot suspicious patterns that once took hours to assemble manually. Automated triage now handles routine warnings, reserving human attention for incidents that show genuine signs of intrusion. Leaders say speed matters because attackers can move from an initial breach to data theft very quickly. Specialists following cyber security operations say smaller firms are increasingly buying shared monitoring services rather than building their own centres. That model gives them overnight coverage and access to experienced analysts at a predictable cost. Ransomware remains the most feared threat, but credential theft and supplier compromise are rising concerns. Centres are practising response drills with legal, communications and executive teams so decisions are rehearsed before a real crisis. Regular patching and multi factor authentication still prevent many incidents entirely, a reminder that advanced tools work best on strong basic foundations.
What the Evidence Shows
Analyst recruitment remains difficult, with experienced staff in high demand across finance, health and government. Centres are responding with apprenticeships and clearer progression routes for junior analysts. Automation helps retention by removing repetitive alert checking, but leaders warn against trusting software verdicts without human review. False positives can hide genuine attacks in a flood of notifications, so tuning systems to each organisation environment is continuous work. Threat intelligence sharing between sectors has improved, allowing a warning discovered by one centre to protect many others quickly. Attackers are also using artificial intelligence to craft convincing phishing messages, raising the value of staff training and reporting culture. When employees report suspicious emails early, response teams gain precious time. Budgets are under pressure, yet boards increasingly view monitoring as essential insurance. The centres that perform best combine technology, practised teamwork and honest post incident reviews that turn every scare into a lesson. Reporting and analysis from sources such as MIT Technology Review track the same developments, and specialists following cyber security operations say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around cyber security operations now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for cyber security operations depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
There is a practical lesson in all of this for readers deciding what to do today. Start with the verified facts, be wary of anyone promising certainty, and prefer reversible steps while the evidence is still developing. Circumstances differ by country, income and personal situation, so general guidance should always be weighed against your own context before you act on it in any significant or lasting way.
